Cloud
The Rise of LLMJacking: How Threat Actors Monetize Compromised Cloud and Model Resources
Attackers target enterprise large language model deployments across cloud platforms to exploit compute resources
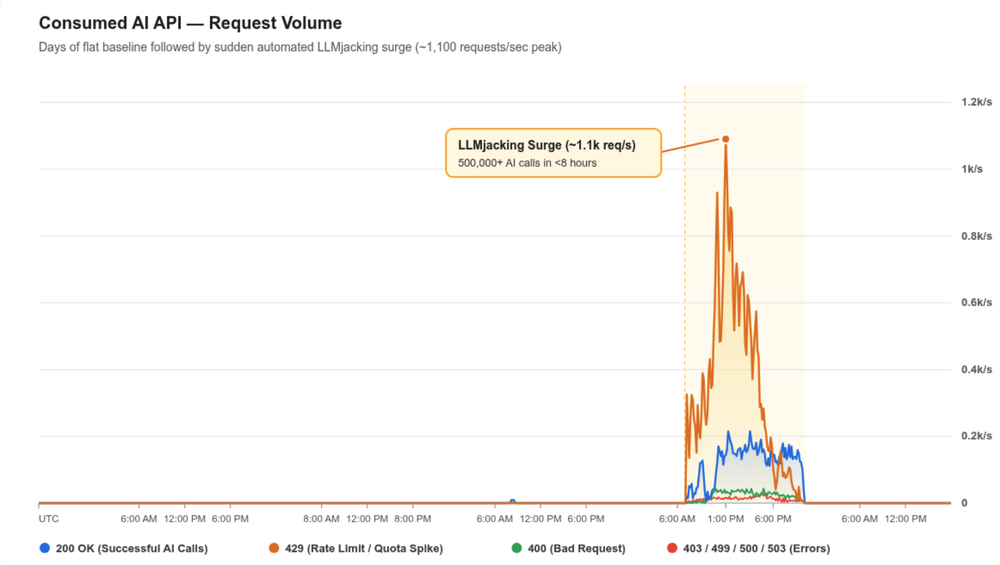
Cybersecurity investigators at Mandiant have reported multiple intrusions involving the hijacking of enterprise access to large language models, a tactic termed LLMJacking. The attacks targeted businesses across financial services, retail and technology sectors throughout North America, South America and the Asia-Pacific region. Threat actors exploited enterprise credentials across various cloud environments to monetise model compute power directly.
Original source
This summary was written by the GPU Data Hub desk from reporting published by Google Cloud Blog on 2 Nov 2026, 14:00. Read the full article at the original publisher.
Read Original Source →